Advanced
2012-03-30
Oracle Security Alert for CVE-2011-5035 OC4J
 2012-03-30 12:05
今早收到Oracle的安全警告邮件,对CVE-2011-5035进行更新
此前于2012年1月31日发布的CVE-2011-5035安全补丁,由于又爆出安全漏洞,所以再次更新,发出安全警告。
邮件内容如下:
Products such as Oracle Audit Vault, Oracle Database, Oracle Enterprise Manager Grid Control and Oracle Identity Management include Oracle Containers for J2EE (OC4J). OC4J is affected by CVE-2011-5035, so security patches need to be applied to OC4J instances in these products
Oracle强烈推荐用户应用这个安全修正。
此前于2012年1月31日发布的CVE-2011-5035安全补丁,由于又爆出安全漏洞,所以再次更新,发出安全警告。
邮件内容如下:
Dear Oracle Customer,该安全漏洞影响包含了OC4J的产品,包括Oracle Audit Vault,Database,OEM,OIM等产品:
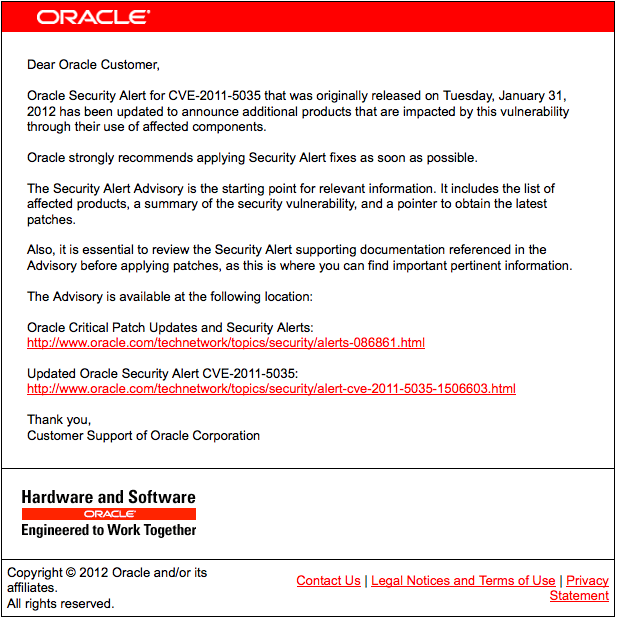
Oracle Security Alert for CVE-2011-5035 that was originally released on Tuesday, January 31, 2012 has been updated to announce additional products that are impacted by this vulnerability through their use of affected components.
Oracle strongly recommends applying Security Alert fixes as soon as possible.
The Security Alert Advisory is the starting point for relevant information. It includes the list of affected products, a summary of the security vulnerability, and a pointer to obtain the latest patches.
Also, it is essential to review the Security Alert supporting documentation referenced in the Advisory before applying patches, as this is where you can find important pertinent information.
The Advisory is available at the following location:
Oracle Critical Patch Updates and Security Alerts:
http://www.oracle.com/technetwork/topics/security/alerts-086861.html
Updated Oracle Security Alert CVE-2011-5035:
http://www.oracle.com/technetwork/topics/security/alert-cve-2011-5035-1506603.html
Thank you,
Customer Support of Oracle Corporation
Products such as Oracle Audit Vault, Oracle Database, Oracle Enterprise Manager Grid Control and Oracle Identity Management include Oracle Containers for J2EE (OC4J). OC4J is affected by CVE-2011-5035, so security patches need to be applied to OC4J instances in these products
这个安全漏洞会导致不需要用户名和密码的访问攻击,通过网络攻击者可以对Weblogic和OAS等产品进行侵入,由于HASH碰撞导致的安全风险可能使用户遭受安全风险。
This security alert addresses the security issue CVE-2011-5035, a denial of service vulnerability in Oracle WebLogic Server, Oracle Application Server (component: Oracle Container for J2EE/OC4J) and Oracle iPlanet Web Server due to hashing collisions. This vulnerability may be remotely exploitable without authentication, i.e., it may be exploited over a network without the need for a username and password. A remote user can exploit this vulnerability to affect the system availability.
Oracle强烈推荐用户应用这个安全修正。
历史上的今天
- 2019-03-30 2015 数据库Gartner市场份额-Oracle 45.6% 占据领先优势
- 2017-03-30 Oracle 11g 密码延迟认证与 library cache lock 等待
- 2011-03-30 恩墨科技2011性能优化培训成功结束
- 2009-03-30 关于ocssd进程的三言两语
- 2008-03-30 resize datafile 与 checkpoint
- 2008-03-30 《深度解析Oracle》之《从等待分析开始》
- 2008-03-30 参加 2008 CSDN 第二次英雄会有感
- 2006-03-30 广告: 招聘SQL SERVER DBA
- 2005-03-30 使用RMAN进行基于表空间的恢复
- 2005-03-30 如何从自动备份中恢复控制文件和SPFILE文件
- 2005-03-30 通过Oracle10g的flashback transaction query新特性进行事务撤销
- 2005-03-30 Oracle10g的Flashback version Query
- 2005-03-30 使用Oracle10g的Flashback Query进行数据闪回